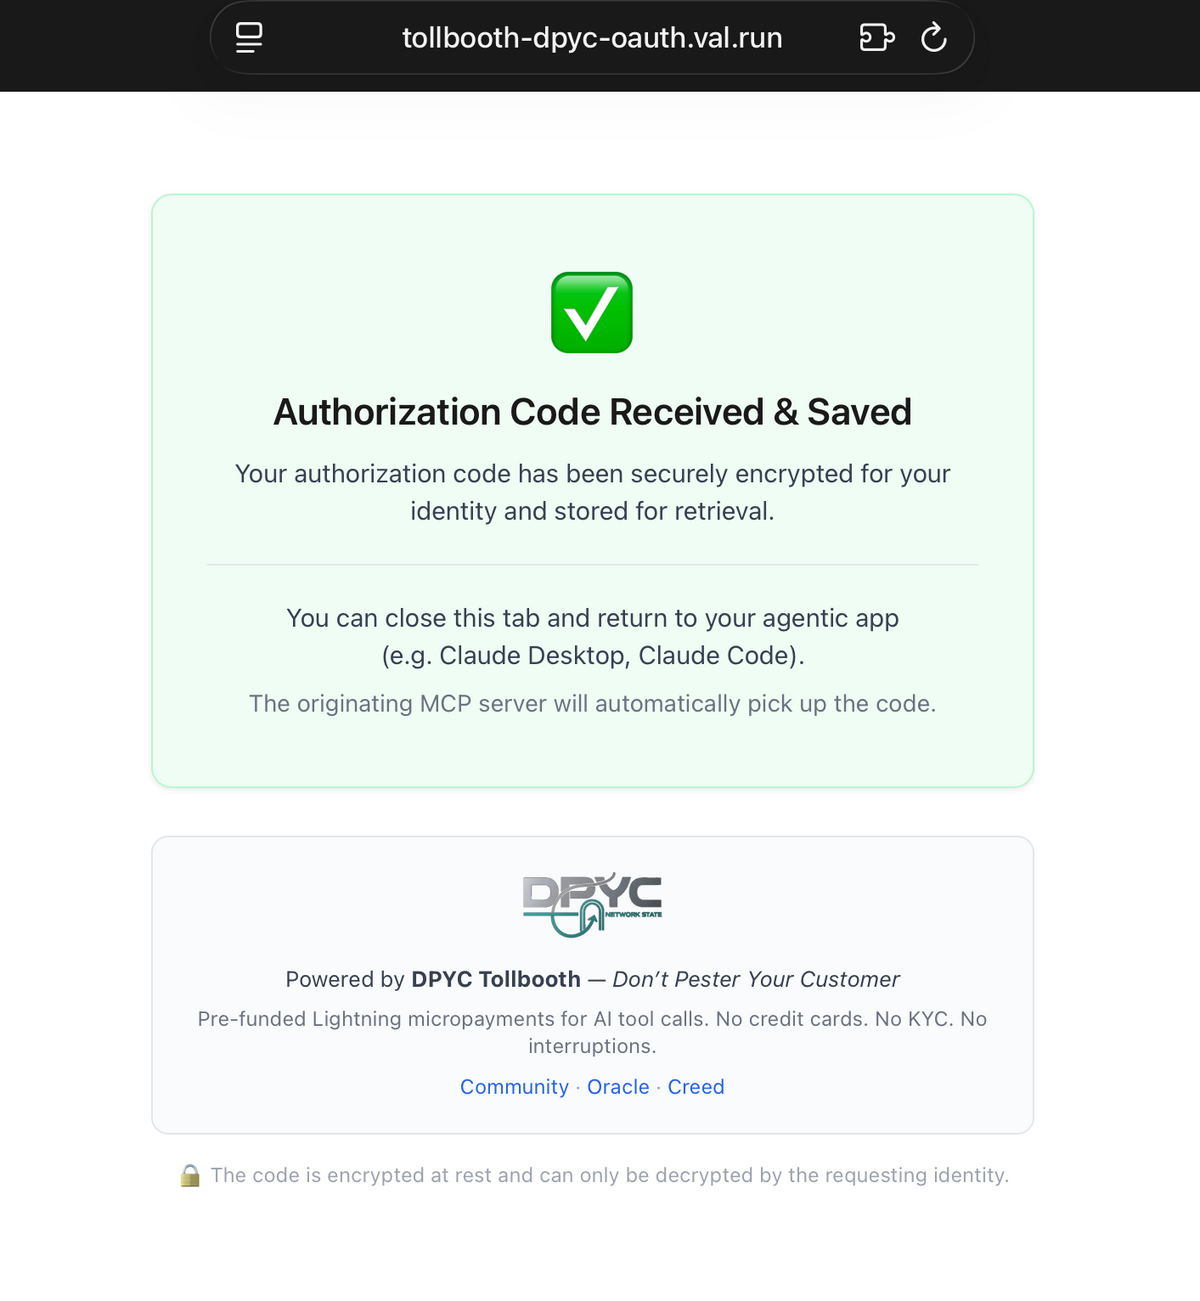
A community utility that solves one narrow, genuinely irritating problem. OAuth2 was designed for browsers, and an agent authorizing against a third-party service has a tool call where the provider expects a redirect handler. The collector supplies the missing piece: a serverless callback receives the redirect from the OAuth provider, stores the code, and an MCP tool retrieves it so the agent can complete the exchange.
Two halves, one job. A callback endpoint that catches the browser redirect, and an MCP interface that hands the code to whoever was waiting for it. Free, shared, and used across the fleet wherever a patron has to authorize an Operator against an account of their own.
It pairs naturally with Tollbooth Shortlinks, since an OAuth redirect URL is exactly the sort of unreadable string a patron should never have to retype on a phone.
At a glance
🔓 Apache 2.0, every line of it
🔌 Built on FastMCP 3.4.7 — any compliant MCP client connects
🤝 Honors the DPYC Social Contract
🆓 Free. Codes are held only long enough for the agent to collect them
Links
 GitHub: lonniev/tollbooth-oauth2-collector
🔌 Connect: tollbooth-oauth2-collector.fastmcp.app
↩ Callback: tollbooth-dpyc-oauth.val.run